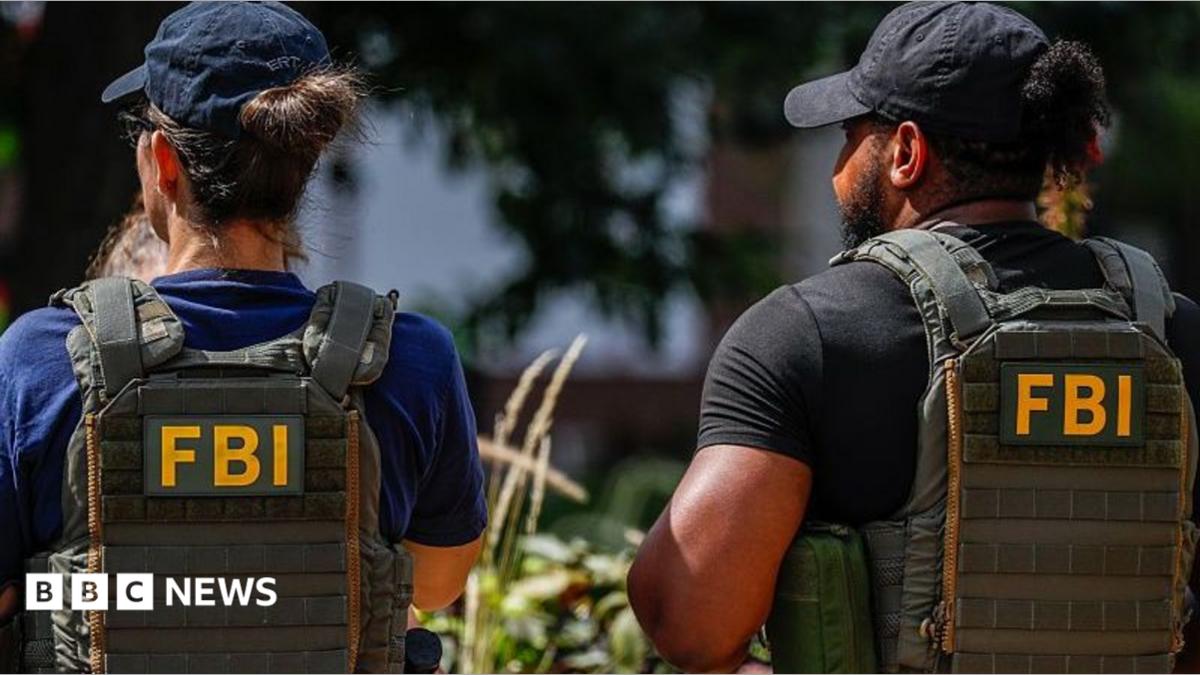
Allied counterintelligence services across Europe and North America are coordinating a major forensic investigation into a state-sponsored cyber intrusion that breached sensitive diplomatic personnel files.
The intrusion, which evaded commercial detection mechanisms for several months, gained access to scheduling software, encrypted travel manifests, and background clearance dossiers of senior diplomats, trade envoys, and defense attachés.
Cyber forensics teams trace the attack to an advanced persistent threat (APT) syndicate utilizing sophisticated living-off-the-land techniques and zero-day firmware exploits on perimeter network firewalls.
"This was not commercial cybercrime; it was a patient, state-sponsored intelligence operation aimed at compromising diplomatic leverage."— National Counterintelligence and Security Center Briefing
Emergency Infrastructure Hardening
In response, allied foreign ministries have initiated emergency hardware replacement across foreign missions, mandating hardware-enforced cryptographic tokens and out-of-band communication protocols for all confidential bilateral negotiations.
Inquiries and discussions must maintain diplomatic civility, analytical depth, and factual accuracy.
Sign in with your Google account to contribute to diplomatic discussions
No reader commentary yet
Be the first verified reader to submit your diplomatic dispatch or critique.